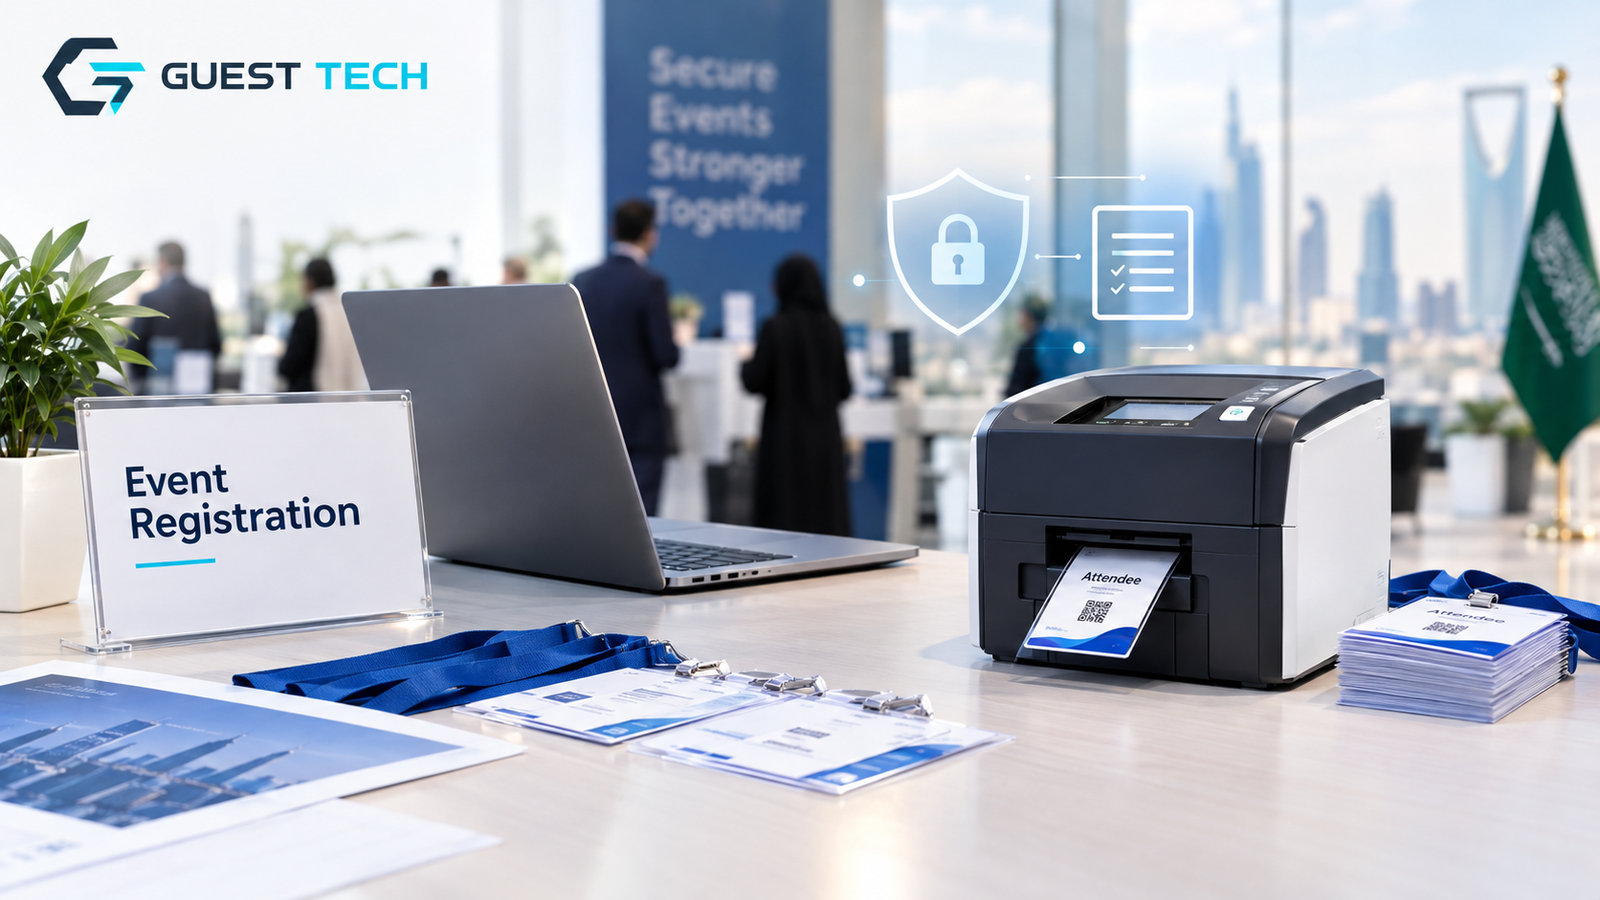
Picture a registration desk at seven in the morning. A few hundred names, phone numbers, company details, and, for the secure sessions, national ID numbers are sitting in a spreadsheet somewhere. Every one of those records falls under Saudi Arabia's Personal Data Protection Law (PDPL). The Saudi Data and AI Authority (SDAIA) is the competent authority for the framework, and its official PDPL knowledge centre is where the law and its implementing regulations live.
Most teams don't think about any of this until something goes wrong, usually a badge list that ends up with the wrong sponsor. If you're still picking a setup, Guest-Tech's registration and check-in solutions can help you decide which fields to collect and how to handle the data from day one.
Practical checks before an audit
Here's the honest part first: we couldn't find an SDAIA checklist built for event registration. What follows is practical guidance based on PDPL's obligations. It isn't an official audit list, and it shouldn't be treated as one.
Start with purpose. If you can't explain why a field exists, take it off the form. A company name on a badge has an obvious reason to be there. A passport number on a general conference form usually doesn't. ID documents need extra caution. Under Article 31 of the Implementing Regulation, controllers should not photocopy identity documents issued by public entities, unless a competent public authority requests the copy or a law requires it. If a copy does get taken, it has to be protected and destroyed once it's no longer needed, unless the law says otherwise.
The privacy notice is the thing attendees will actually read, so make it useful. Put it where people see it before they submit anything. Say who the controller is and how to reach them. Explain why you're collecting the data and on what legal basis. Say how long you'll keep it, who gets it, and which fields are optional. Then explain how to use their rights: access, a copy of their data, correction, and destruction. Each of those comes with conditions under the law, so don't promise a yes to every request.
On retention, PDPL doesn't give you a fixed number of days. The data can stay only as long as the purpose or a legal requirement needs it. Write a schedule down, and delete or anonymize on that schedule. Records of processing activities are a separate matter and must be kept for five years after the activity ends.
Access is where audits tend to turn up problems. Every staff member should log in with their own account, with permissions that match their job. Keep exports to people who genuinely need them. And when a temporary worker's contract ends, their access should end the same day.
Breaches come with a deadline. If an incident could harm the data or the person, or conflict with their rights, the controller has to notify the competent authority within 72 hours of finding out. Where harm is likely, the people affected need to be told without undue delay. Not every incident clears that bar, but write down how you assessed it either way. Article 24 of the Implementing Regulation has the exact conditions.
Working with vendors
Handing registration to a platform, a badge printer, or a lead scanning app doesn't hand off your responsibility. You're still the controller. The regulation expects you to choose a processor that can give sufficient guarantees, and your contract should cover the purpose, the data types, how long the vendor holds the data, breach notice without undue delay, and any subprocessors. Check compliance from time to time, not only at signing. A processor that goes beyond your instructions can end up treated as a controller itself. Go through agreements, subprocessors, and hosting before registration opens.
Hosting data outside the Kingdom
Sending personal data abroad is covered by PDPL and the Regulation on Personal Data Transfer Outside the Kingdom. Overseas hosting is neither banned nor automatically fine. Look at where the data goes, who receives it, why, and what protections apply. Sensitive data, and transfers that are continuous or large in scale, may require a risk assessment first. The usual safeguards are standard contractual clauses, binding common rules, or an accreditation certificate.
Where Guest-Tech fits in
Guest-Tech handles event registration, accreditation, visitor management, badge printing, and onsite support in Saudi Arabia and across the wider GCC. We're happy to walk through your workflow, field choices, and access roles with your team. What we don't do is issue legal compliance certificates, so have your legal or compliance team confirm what applies to your event. To start that conversation, use the contact page.
Frequently asked questions
Does PDPL apply to small events?
It does. Event size doesn't change the rules. A small event collecting names and contact details is still processing personal data. The paperwork can be lighter, but the obligations are the same.
Do I always need consent?
No. Consent is one lawful basis, not the only one. Legitimate interest is another, but it takes a documented assessment and can't be used for sensitive data. Work out the right basis for each purpose separately.
If a vendor leaks data, whose problem is it?
It's still yours as the controller, though the vendor has its own duties under the contract and the law. Your contract and incident procedure are what settle who does what, so make sure both are written down.
How long should I keep registration data?
Only as long as the purpose needs it, or as long as the law requires. Put that period in your privacy notice and your schedule. When it runs out, destroy or anonymize the data.
Set up registration properly before the first attendee signs up
Talk to Guest-Tech about registration workflows, access controls, and data handling for your next event in Saudi Arabia.
Request a Quote